
Bitcoin mining did not start with Bitcoin.More than a decade before the Bitcoin network launched, cryptographer Adam Back proposed a system called Hashcash that required computers to perform computational work before certain digital actions could be completed. Hashcash was designed to combat email spam and denial-of-service attacks, not to create digital money.
Yet one part of that idea became fundamental to Bitcoin.
Hashcash showed that computation could be turned into a measurable cost: difficult to produce but relatively easy to verify. In 2008, Satoshi Nakamoto cited Adam Back’s Hashcash in the Bitcoin whitepaper and adapted its proof-of-work concept for a completely different problem: how to maintain a shared transaction history without a central authority.
The connection between Hashcash and Bitcoin comes from proof of work. Both systems use computational effort as something that is costly to produce but easy for others to verify.
Bitcoin combined that proof-of-work idea with cryptographic signatures, blocks, a peer-to-peer network, mining incentives, and a difficulty-adjustment mechanism.
Hashcash made computation costly. Bitcoin turned that cost into a tool for securing a decentralised monetary network.
Understanding what Hashcash is and how it shaped Bitcoin’s design explains why miners search for nonces, why the network uses a target, and why changing an established block requires substantial computational work.
Hashcash is a proof-of-work system created by Adam Back in 1997. Its original purpose was to make certain forms of online abuse more expensive by requiring a computer to perform computational work before an action could be completed.
The problem was straightforward.
Sending one email costs almost nothing computationally. Sending millions of emails can also be cheap for an automated spam operation. If every message required a small amount of computational work, sending a few legitimate messages would remain practical while sending millions would require significantly more computing resources.
Hashcash introduced an important asymmetry:
Finding a valid proof: Computationally expensive
Checking a valid proof: Computationally inexpensive
That asymmetry is the defining characteristic of proof of work.
Back later documented Hashcash in his 2002 paper, *Hashcash: A Denial of Service Counter-Measure*. The system was intended to impose a computational cost on activities such as email spam, anonymous remailers, and other forms of systematic abuse.
The important idea was not the particular application. It was that computation could be used as a scarce resource.
That concept later became highly relevant to Bitcoin.
Hashcash belongs to a longer history of research into computational proof of work.
In 1992, Cynthia Dwork and Moni Naor explored the use of computational pricing to combat junk mail. Their work helped establish an important theoretical foundation for using computational effort as a cost for digital actions.
Adam Back later developed Hashcash into a practical proof-of-work mechanism for internet protocols.
The concept was useful because it did not require users to make a direct monetary payment. A legitimate user could spend a small amount of computing power to generate a proof, while a spammer attempting to send millions of messages would have to repeat that computational cost on a much larger scale.
Hashcash was therefore an early practical example of using computational scarcity rather than direct financial payment to control digital activity.
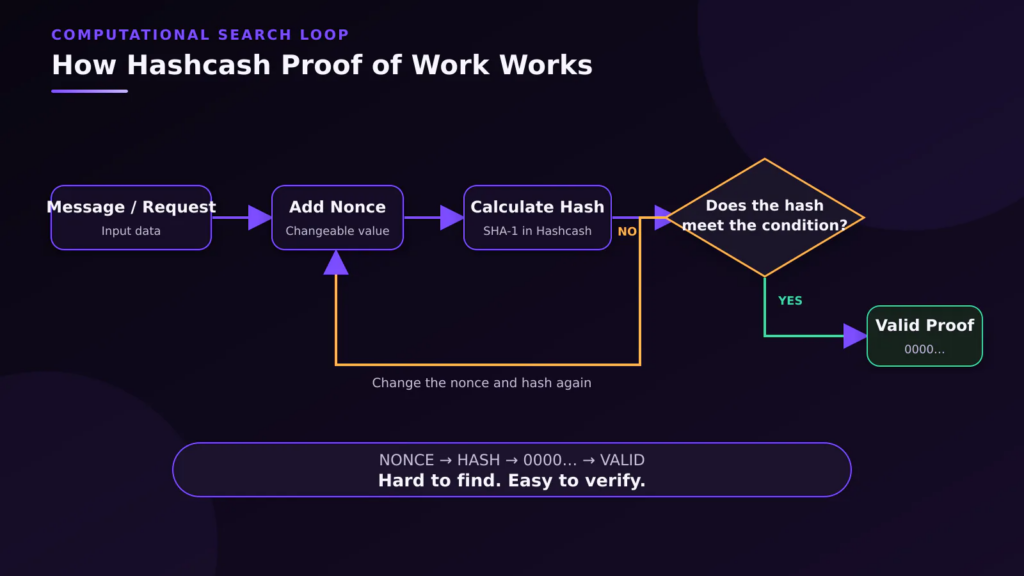
Hashcash uses a cryptographic hash function to create a computational search problem.
A cryptographic hash function turns input data into a fixed-length string of characters called a hash. Even a tiny change to the input produces a completely different-looking result.
A system can require the resulting hash to satisfy a specific condition. The computer then changes a value such as a counter or nonce and hashes the data repeatedly until it finds a valid result.
For example, imagine a simplified Hashcash system requiring a hash to begin with four zeros:
Nonce 1 → Hash → Invalid
Nonce 2 → Hash → Invalid
Nonce 3 → Hash → Invalid
Nonce 4 → Hash → Invalid
Nonce 5 → Hash beginning with 0000 → Valid
The computer cannot know in advance which nonce will produce a valid result. It has to search through possible values.
Once a valid result is found, another computer can verify it by calculating the hash and checking whether it meets the required condition.
This creates the fundamental proof-of-work relationship:
Expensive to find → Easy to verify
The original Hashcash design used SHA-1. Bitcoin later adapted the same general proof-of-work principle using double SHA-256.
The usefulness of Hashcash comes from making computation expensive enough to discourage abuse without making verification expensive.
Imagine a system requiring one second of computation for every email.
For an ordinary user sending 20 emails, the total cost might be manageable. For a spammer attempting to send 10 million messages, the same requirement becomes a much larger operational burden.
Hashcash therefore changes the economics of automated abuse.
It does not make spam mathematically impossible. Instead, it makes large-scale abuse more resource-intensive.
Bitcoin uses the same economic principle in a different setting.
Bitcoin does not attempt to prevent miners from performing proof of work. It deliberately makes them compete to perform it. The computational cost becomes part of the network’s security model.
Hashcash became directly relevant to Bitcoin because Satoshi Nakamoto cited it in the original Bitcoin whitepaper.
In the paper’s proof-of-work section, Satoshi describes a system similar to Adam Back’s Hashcash as part of Bitcoin’s approach to creating a distributed timestamp server on a peer-to-peer network.
The whitepaper explains that participants search for a value that produces a hash meeting a required condition. It also explains that changing a completed block requires the proof of work to be performed again.
However, Bitcoin did not simply copy the original Hashcash protocol.
The two systems were designed for different problems.
| Hashcash | Bitcoin |
|---|---|
| Makes spam and abuse computationally expensive | Makes block production and history manipulation computationally expensive |
| Proof attached to an individual request or message | Proof attached to a block header |
| Originally designed for anti-spam and denial-of-service protection | Designed for decentralised electronic cash |
| No blockchain | Uses a chain of blocks |
| No mining reward | Miners receive block subsidy and transaction fees |
| Work factor for individual actions | Network-adjusted proof-of-work target |
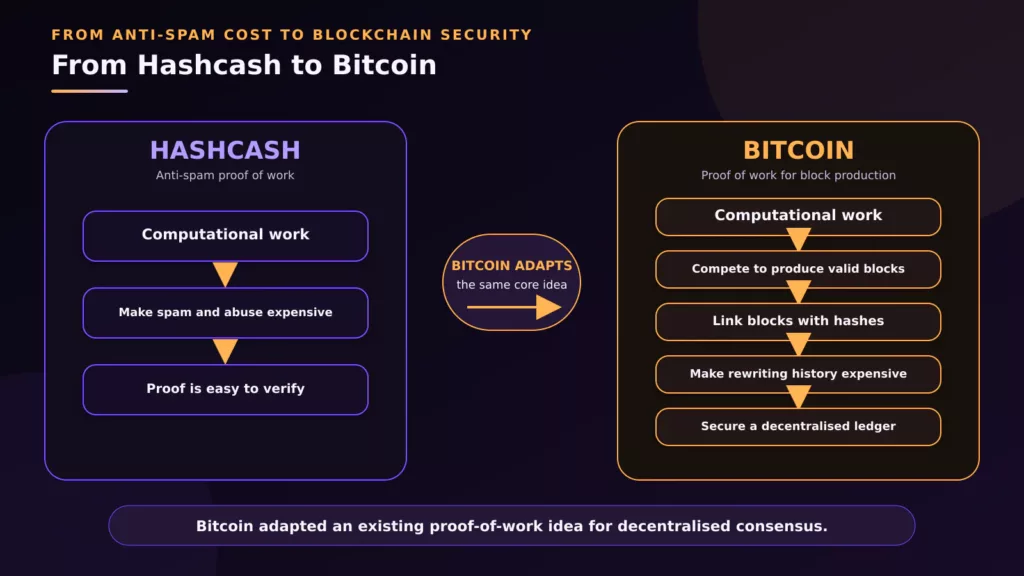
The key connection is simple:
Hashcash demonstrated that computational work could create a measurable digital cost. Bitcoin adapted that property to block production and decentralised consensus.
Bitcoin attaches proof of work to blocks, rather than individual email messages or service requests.
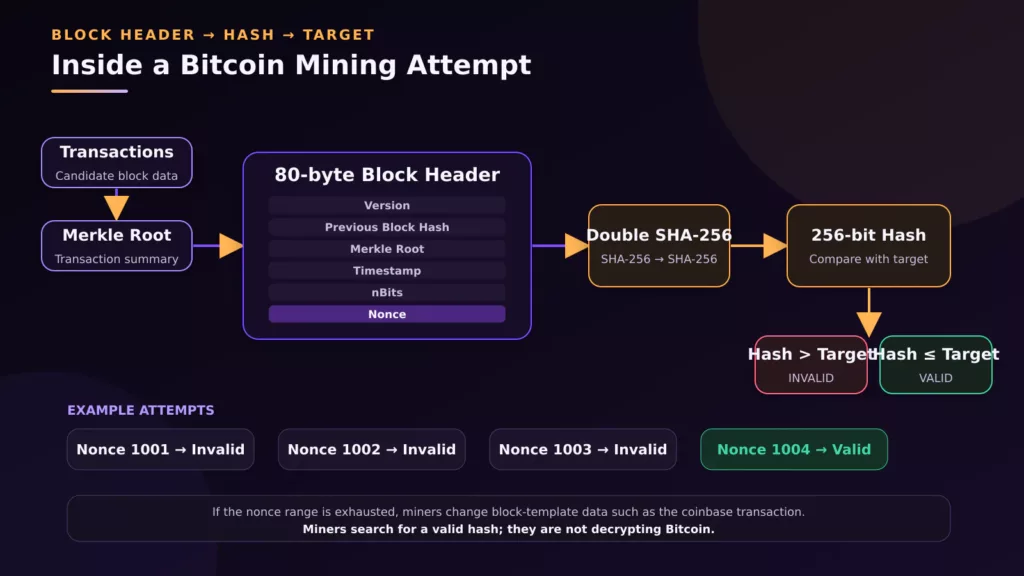
A miner builds a candidate block containing transactions and constructs an 80-byte block header.
The block header contains six fields:
The Merkle root summarises the transactions included in the block. The previous block hash links the new block to its predecessor. The nBits field encodes the target threshold used for proof-of-work validation.
The miner repeatedly hashes the block header using Bitcoin’s proof-of-work algorithm:
SHA-256 → SHA-256
The resulting 256-bit value is interpreted as a number.
For the proof of work to be valid, that number must be less than or equal to the target.
In simplified form:
Block hash ≤ Target
The target is the actual threshold that determines whether a block satisfies the proof-of-work requirement. Difficulty is a separate measure describing how hard it is to find a valid hash relative to the easiest permitted target.
This distinction matters because beginners often use “difficulty” and “target” interchangeably even though they describe different things.
The nonce gives miners a value they can change while searching for a valid block hash.
A simplified mining attempt might look like this:
Nonce 5001 → Hash → Invalid
Nonce 5002 → Hash → Invalid
Nonce 5003 → Hash → Invalid
Nonce 5004 → Hash → Invalid
…
Nonce 918742 → Hash → Valid
The miner does not know which nonce will work. It keeps trying different values until one produces a hash that falls below the target.
However, modern Bitcoin mining is not limited to the nonce.
The nonce is a 32-bit field, meaning it has a finite range of possible values. Modern mining hardware can search that range very quickly. When miners need a new search space, mining software can modify other parts of the candidate block, particularly data in the coinbase transaction. This changes the Merkle root and produces a new block header to search.
Modern Bitcoin mining therefore involves much more than simply counting upwards from nonce zero.
Bitcoin’s target determines how restrictive the proof-of-work requirement is.
Higher target → More hashes qualify → Easier mining
Lower target → Fewer hashes qualify → Harder mining
Bitcoin stores the target in compact form through the nBits field in the block header.
The network periodically adjusts the target to account for changes in the computational power participating in mining.
Bitcoin adjusts its difficulty every 2,016 blocks, with the system designed to maintain an average block interval of approximately 10 minutes over time.
Hashcash and Bitcoin share the same fundamental proof-of-work principle, but their purposes and implementations are different.
| Feature | Hashcash | Bitcoin |
|---|---|---|
| Creator | Adam Back | Satoshi Nakamoto |
| First proposed | 1997 | 2008 |
| Original purpose | Combat spam and network abuse | Secure decentralised electronic cash |
| Main participant | Email sender or service requester | Bitcoin miner |
| Basic mechanism | Hash-based proof of work | Hash-based proof of work |
| Original hashing | SHA-1 | Double SHA-256 |
| Proof attached to | A request or message | A block header |
| Blockchain | No | Yes |
| Difficulty mechanism | Work factor | Network-adjusted target |
| Mining rewards | No | Block subsidy and transaction fees |
| Consensus role | Not designed as blockchain consensus | Core part of Bitcoin’s consensus system |
| Security goal | Increase the cost of abuse | Increase the cost of producing and rewriting chain history |
The simplest distinction is:
Hashcash makes an individual digital action costly. Bitcoin makes competing blockchain histories costly to produce and rewrite.
Bitcoin’s proof of work is therefore best understood as an adaptation of the Hashcash idea rather than a direct implementation of the original anti-spam protocol.
Bitcoin’s major innovation was placing proof of work inside a chain of blocks.
Each Bitcoin block contains the hash of the previous block’s header.
Consider a simplified chain:
| Block 100 → Block 101 → Block 102 → Block 103 |
|---|
Block 101 commits to Block 100. Block 102 commits to Block 101, and so on.
If an attacker changes a transaction in Block 100, the Merkle root changes. That changes the block header and therefore its proof-of-work hash.
The attacker would then need to produce valid proof of work for the altered Block 100 and continue producing valid blocks afterwards.
The security effect grows as more blocks are added after the transaction.
This does not make rewriting history mathematically impossible. It makes rewriting history computationally expensive.
That distinction is central to understanding Bitcoin’s security model.
Digital signatures can prove that a transaction was authorised by the holder of the relevant private key.
But signatures alone do not solve the double-spending problem.
A user could attempt to create two conflicting transactions that spend the same bitcoin. The network therefore needs a way to establish which transaction belongs in the accepted history.
Bitcoin combines transaction validation, digital signatures, blocks, and proof of work to establish that history.
Miners collect valid transactions into candidate blocks and compete to produce a block that satisfies the current proof-of-work target.
Nodes independently verify proposed blocks and enforce Bitcoin’s consensus rules.
When competing valid chains exist, Bitcoin’s chain-selection mechanism is based on the chain with the most accumulated proof of work, subject to the network’s consensus rules.
This is why the simplified phrase “longest chain” can sometimes be misleading. The relevant measure is accumulated work, not simply the number of blocks.
Proof of work therefore gives the network a computational and economic cost for attempting to replace an accepted transaction history.
Hashcash’s original purpose did not require miners to receive newly created money.
Bitcoin does.
Mining consumes computing resources and electricity, so miners need an economic incentive to participate.
A successful miner can receive:
The block subsidy also forms part of Bitcoin’s programmed issuance schedule.
This creates a feedback loop:
Miners provide computational work
↓
The network uses that work to secure block production
↓
Successful miners receive rewards
↓
Economic incentives encourage continued participation
Hashcash demonstrated that computation could be used as a scarce resource. Bitcoin connected that computational resource to economic incentives and a decentralised ledger.
Bitcoin’s proof-of-work design emerged from a much longer history of cryptographic and digital-cash research.
Cynthia Dwork and Moni Naor explored computational pricing as a way to combat junk mail, helping establish an important theoretical foundation for proof-of-work systems.
Adam Back proposed Hashcash as a proof-of-work mechanism for combating email spam and other forms of network abuse.
Back published *Hashcash: A Denial of Service Counter-Measure*, providing a detailed description of the system and its applications.
Hal Finney developed Reusable Proofs of Work (RPOW), exploring how proof of work could be connected to reusable digital tokens and electronic cash.
Satoshi Nakamoto published *Bitcoin: A Peer-to-Peer Electronic Cash System*. The paper explicitly referenced Adam Back’s Hashcash in its proof-of-work section.
The Bitcoin network began operating, turning proof of work into a core component of a live decentralised monetary system.
Adam Back’s role in Bitcoin’s technical history is well documented.He created Hashcash, an important earlier implementation of proof of work, and Satoshi Nakamoto explicitly cited Hashcash in the Bitcoin whitepaper.That makes Back an important figure in Bitcoin’s technical lineage.It does not, however, establish that Back created Bitcoin.
The distinction is straightforward:
Adam Back → Creator of Hashcash
Satoshi Nakamoto → Pseudonymous creator of Bitcoin
Adam Back has also been the subject of speculation about whether he is Satoshi Nakamoto. Those claims remain unproven, and Back has denied being Bitcoin’s creator.
For understanding Bitcoin’s design, the speculation is less important than Back’s documented contribution: Hashcash helped establish the proof-of-work concept that Satoshi later adapted.
Bitcoin’s relationship with Hashcash is best described as adaptation rather than simple copying.
Hashcash established several properties that were useful to Bitcoin:
Bitcoin placed those properties into a completely different architecture.
Hashcash attached proof of work to individual actions such as email.Bitcoin attaches proof of work to block headers containing commitments to transaction data.
Hashcash proofs were not designed to create a continuously growing blockchain.Bitcoin links blocks through previous-block hashes, creating a history where changing an earlier block affects every block that follows it.
Bitcoin operates in an environment where mining hardware and participation can change.The protocol therefore adjusts its target every 2,016 blocks to regulate the average pace of block production.
Hashcash imposed a computational cost on the user generating the proof.Bitcoin turns proof of work into competition between miners, with successful block producers receiving block rewards and transaction fees.
These adaptations are what made proof of work useful for a decentralised monetary network.
Hashcash matters because it provides important context for understanding where Bitcoin’s mining mechanism came from.Bitcoin was not created in isolation.Its design drew on earlier work involving cryptographic hashing, proof of work, digital signatures, electronic cash, privacy, and distributed systems.Hashcash contributed one particularly important idea:
Computation can be turned into a measurable and verifiable cost.
Satoshi used that concept in a new setting.Instead of relying on a central authority to decide which transaction history was valid, Bitcoin uses proof of work to make block production competitive and blockchain history costly to rewrite.
Instead of allowing an attacker to gain influence simply by creating many identities, Bitcoin ties block-production influence to computational work.Hashcash did not provide Bitcoin’s blockchain, transaction model, mining incentives, or complete consensus rules.Its contribution was narrower and still highly significant.
Hashcash provided an important proof-of-work building block. Bitcoin turned that building block into part of a decentralised consensus system.
Hashcash was created to make spam expensive. Bitcoin adapted the same core proof-of-work idea to make blockchain history expensive to manipulate.
Adam Back’s Hashcash demonstrated that computational work could create a measurable cost without requiring a central authority. More than a decade later, Satoshi Nakamoto adapted that principle for Bitcoin.
But Bitcoin went much further.
It combined proof of work with cryptographic signatures, linked blocks, transaction validation, mining incentives, and a difficulty-adjustment system. The result was a decentralised network in which miners compete to produce blocks and participants can independently verify the rules governing the ledger.
That is the real connection between Hashcash and Bitcoin.
Hashcash supplied an important proof-of-work building block. Bitcoin gave that building block a new purpose: helping a decentralised network maintain a shared monetary history.
Bitcoin did not invent proof of work. It adapted an existing cryptographic idea and combined it with other technologies to create something fundamentally different from Hashcash’s original anti-spam system.From fighting spam to securing digital money, the history of proof of work shows how an existing cryptographic idea can become the foundation for an entirely new system.
Hashcash is a proof-of-work system created by Adam Back in 1997. It was designed primarily to make email spam, denial-of-service attacks, and other forms of systematic online abuse more expensive by requiring computational work.
Adam Back created Hashcash in 1997. He later published a detailed description of the system in his 2002 paper, *Hashcash: A Denial of Service Counter-Measure*.
Hashcash was developed to impose a computational cost on activities that were otherwise cheap to perform at large scale, particularly email spam and denial-of-service abuse.
A computer repeatedly changes a value such as a nonce and hashes the resulting data until the hash satisfies a predefined condition. The successful result acts as proof that computational work was performed.
Bitcoin did not simply implement the original Hashcash protocol. Satoshi Nakamoto adapted its underlying proof-of-work concept for Bitcoin’s block-mining and decentralised consensus system. The Bitcoin whitepaper explicitly describes its proof-of-work system as similar to Adam Back’s Hashcash.
Hashcash demonstrated that computational work could be expensive to produce but inexpensive to verify. Bitcoin adapted this property so miners compete to produce valid blocks and make rewriting blockchain history computationally costly.
Hashcash was primarily designed to make spam and network abuse expensive. Bitcoin’s proof of work is used to secure a blockchain, provide Sybil resistance, regulate block production, and increase the cost of rewriting transaction history.
Adam Back created Hashcash, an important predecessor to Bitcoin’s proof-of-work mechanism. Satoshi Nakamoto cited Hashcash in the original Bitcoin whitepaper, making Back a significant figure in Bitcoin’s technical history.